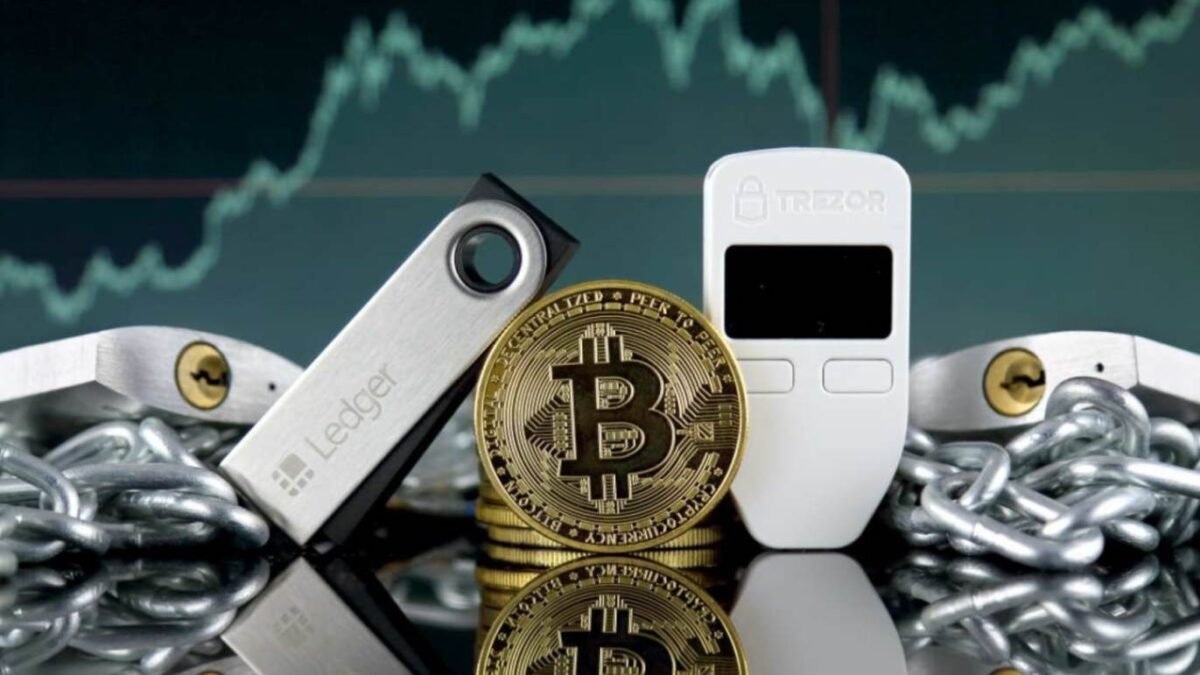
Anyone selling a crypto wallet into the European Union now has 24 hours to tell a regulator when a vulnerability in their product is being actively exploited.
The reporting obligations under the EU’s Cyber Resilience Act took effect on 11 September. They apply to all products with digital elements made available in the EU, and the European Commission has confirmed that includes devices already on the market.
What Actually Triggers the Clock
The scope is narrower than the coverage suggests, and the distinction matters.
The Commission’s wording is that manufacturers must report actively exploited vulnerabilities and severe incidents ‘that have an impact on the security of their products.’ The obligation attaches to the product, not to the company.
That is a meaningful line. A flaw in a hardware wallet’s firmware that lets an attacker recover private keys sits squarely inside it. A data breach at a company’s shipping contractor, exposing customers’ names and addresses, is a serious event but it is not a vulnerability in the product, and on the face of the regulation it appears to fall outside. Whether a given incident qualifies is ultimately a legal question rather than an editorial one.
So this is not a general breach-disclosure regime. It is a product security regime that happens to catch wallets because a wallet is a product with digital elements.
The Timetable and the Penalties
The sequence runs in three stages. An early warning within 24 hours of awareness. A full notification within 72 hours. Then a final report, due no later than 14 days after a corrective or mitigating measure becomes available for an actively exploited vulnerability, or within one month for a severe incident.
Notifications go through a single reporting platform built and run by ENISA, the EU’s cybersecurity agency, with national market surveillance authorities responsible for enforcement.
The Act sets administrative fines of up to 15 million euros, around $17.3 million, or 2.5% of worldwide annual turnover, whichever is higher, for breaches of the relevant obligations. Supplying incorrect, incomplete or misleading information carries a separate penalty of up to 5 million euros.
Where This Meets the 90-Day Argument
Last week Ledger’s chief technology officer Charles Guillemet and Trezor’s head of security Jan Komárek both made the case for coordinated disclosure, arguing that researchers should report privately and allow a 90-day window before publishing. Guillemet called premature publication attention farming with someone else’s risk.
The two rules are not in conflict, and it is worth being precise about why. The 24-hour clock is notification to a regulator. The 90-day window concerns publication to the world. A vendor can comply with both.
But something has changed. Under a 90-day coordinated disclosure, the vendor and the researcher were the only parties who knew a flaw existed until a patch shipped. From 11 September, in Europe, a regulator knows within a day.
That does not put the information in public hands, and ENISA is not a publisher. It does mean the vendor is no longer the sole holder of the timetable, and that an incident which goes unpatched for months is now visible to someone with enforcement powers while it stays invisible to customers.
What This Phase Is and Is Not
One detail has gone largely unreported and it changes how much of the Act is actually live.
The reporting obligations started on 11 September. The main obligations, covering how products must be designed, updated and maintained, and the CE marking that will identify compliant devices, do not apply until 11 December 2027.
So what has arrived is the alarm system, not the building code. Manufacturers must now tell a regulator quickly when something is being exploited. What they must do to prevent it in the first place is fifteen months away.