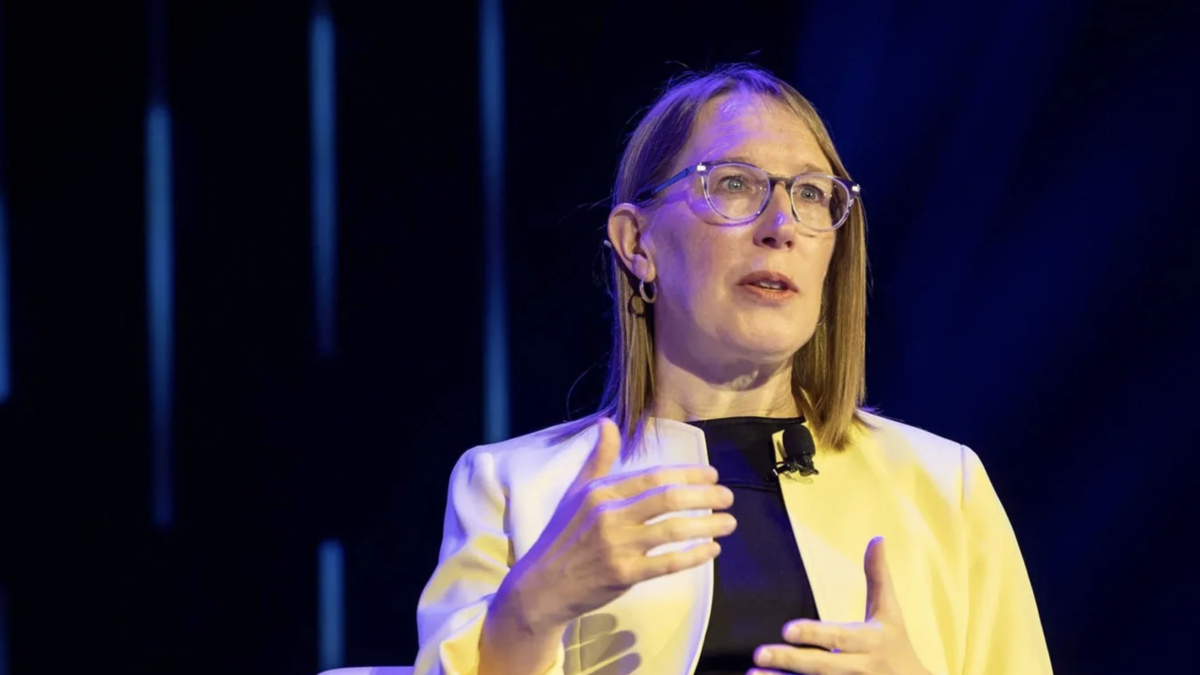
Hester Peirce used a SIFMA appearance on Wednesday to argue that financial surveillance has stopped working.
She called the current framework a panopticon, said its cost dwarfs what it achieves, and set out four specific changes she wants made.
Most of the rules she described are not written by the agency she sits on.
What She Said
The remarks, delivered on 23 September at SIFMA’s Digital Assets Conference under the title “Looking for Change in Haystacks,” carried her standard footnote that the views are her own and not necessarily the Commission’s.
Her objection is to accumulation for its own sake. “We build ever bigger data haystacks on the theory that we will find a needle or two inside,” she said. “The bigger haystack, however, makes it harder to find the needles.” On the machinery of customer identification programmes, currency transaction reports and suspicious activity reports, she was blunter still, saying its expense “seems to dwarf its effectiveness at stopping bad actors.”
The status quo, as she put it, means “more data collection, more intermediary surveillance, more ‘know your customer’ requirements that turn our financial rails into a panopticon.”
Her alternative is cryptographic. “A zero-knowledge proof can tell a counterparty ‘Yes, this person meets your requirement’ without that counterparty knowing your name, income, or address.” Verifiable credentials could attest to age, citizenship, accredited investor status or absence from a sanctions list without handing over the underlying file.
The Four Asks
She wants attribute-based verification wherever it is technologically feasible, rather than prescriptive collection mandates. She wants registered firms allowed to rely on third-party identity verification, so the same documents are not copied into dozens of institutions. She questions whether the dollar thresholds triggering transaction reports are set too low. And she wants room for tools that operate without an identifiable intermediary at all.
Whose Rules These Are
Customer identification, currency transaction reports and suspicious activity reports are obligations of the Bank Secrecy Act, administered by the Financial Crimes Enforcement Network at Treasury. The customer identification rule that applies to broker-dealers is a FinCEN rule.
The SEC’s own anti-money-laundering guidance states the position without ambiguity. The Commission does not independently issue AML rules. Its instrument is a single Exchange Act rule requiring broker-dealers to comply with the ones Treasury wrote, with FINRA supplying the programme requirements underneath.
Peirce’s speech does not name the Bank Secrecy Act, FinCEN, Treasury or Congress anywhere in its text, though a footnote cites a Cato Institute analysis questioning how well FinCEN reporting works. Reporting thresholds in particular are not hers to move.
What Is Actually in Reach
One ask has a plausible route. Reliance on third-party verification is shaped in practice by how the SEC examines firms and what relief it is willing to grant, which is Commission territory even where the rule is not.
The timing matters for the rest. Peirce leaves in November, a move announced in June, and she titled a speech earlier this month “Lame Duck.”
The argument is serious and well made. The address on the envelope is the problem.